Key Takeaways
- Manufacturing was the most-attacked industry globally in 2025 for the fifth consecutive year, accounting for more than a quarter of all incidents IBM’s X-Force team responded to.
- Data theft, not disruption for its own sake, was the most common objective behind these incidents.
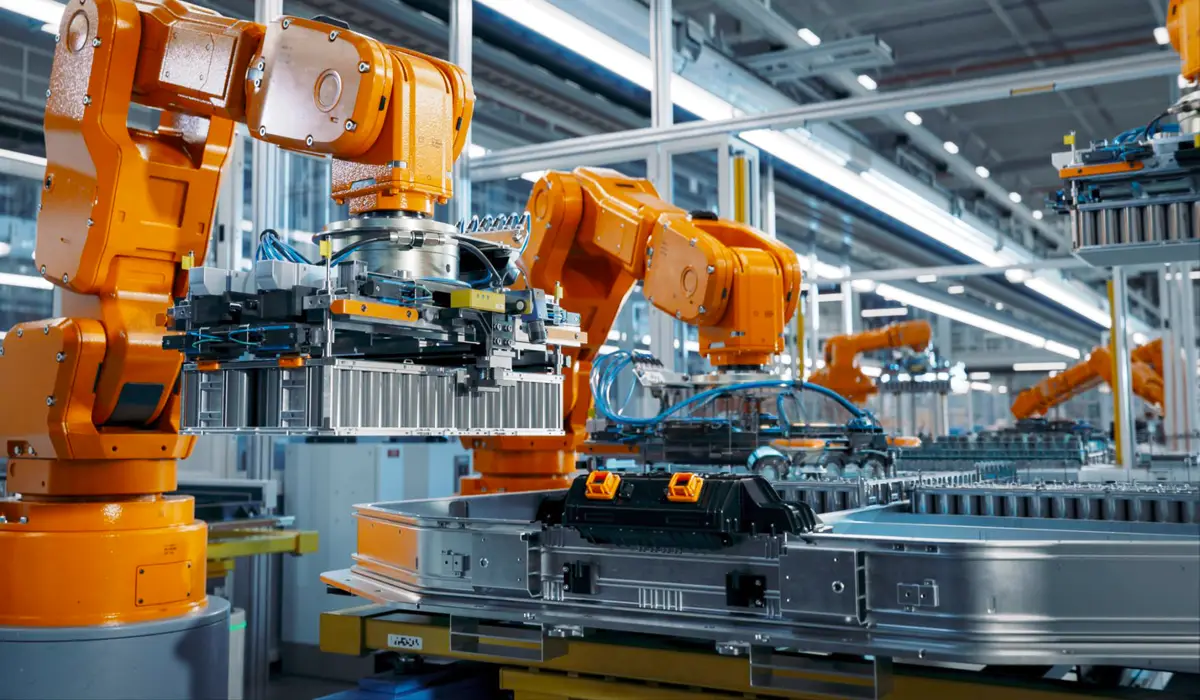
- Manufacturers face a wider attack surface than a typical office environment: standard IT systems plus operational technology (OT), the factory equipment and industrial controllers that keep production running.
- Exploiting public-facing systems overtook stolen credentials as the leading way attackers get in, a shift driven partly by AI-assisted vulnerability discovery.
- A unified manufacturing cybersecurity approach across IT, OT, and connected products, rather than treating each as a separate problem, is what separates manufacturers who recover quickly from those who don’t.
The Industry That Attackers Keep Coming Back To
If asked to guess the most-targeted industry for cyberattacks, most people reach for banking. It’s a reasonable guess, and it’s wrong. According to IBM’s 2026 X-Force Threat Intelligence Index, manufacturing held the top spot for the fifth year running, accounting for 27.7% of all incidents IBM’s team responded to globally in 2025, ahead of financial services and insurance.
As IBM’s own analysis of the finding put it, the explanation isn’t that manufacturers hold more valuable data than banks. It’s that manufacturers offer more ways in, and a successful attack costs them more, faster, than it costs most other industries.
Two Attack Surfaces Instead of One
A typical office-based business has one attack surface to defend: the IT environment. A manufacturer has two. There’s the standard IT side, email, file servers, the ERP system, and there’s operational technology, the programmable logic controllers, sensors, and industrial computers that actually run the production line. Those two environments were built decades apart, for different purposes, by different teams, and they’ve been getting connected to each other at a rapid pace as “smart factory” initiatives push for real-time data flowing from the sensor to the front office.
That connectivity is genuinely valuable. It also means a foothold gained on the IT side, through something as mundane as a phishing email, now has a plausible path toward systems that were never designed with an attacker in mind. OT equipment often runs for fifteen or twenty years without a security patch, because the priority when it was built was reliability and safety, not resistance to network intrusion.
What Attackers are Actually After
Contrary to the ransomware-lockout image most people carry, data theft was the most common goal behind manufacturing incidents in IBM’s data, not encryption for its own sake. Product designs, proprietary processes, supplier contracts, and customer data all have resale or leverage value, and manufacturers frequently hold all four.
The way attackers get that first foothold has also shifted. IBM found that exploiting public-facing applications, things like a company website, a customer portal, or an internet-connected device, overtook stolen credentials as the leading initial access method for the first time in the report’s history, a change IBM ties partly to AI tools that let attackers scan for and exploit vulnerabilities far faster than manual methods allowed. Manufacturers, with their sprawling mix of internet-facing dashboards, remote-access tools for vendors, and connected equipment, present an unusually large version of exactly that target.
Why Downtime is the Real Number that Matters
For most businesses, a cyber incident means a disrupted week and an uncomfortable conversation with customers. For a manufacturer, it can mean a stopped production line, missed delivery windows tied to contractual penalties, and idle labor that keeps costing money whether or not anything is being produced. The financial exposure isn’t abstract. It’s measured in dollars per hour of downtime, and it starts accumulating the moment systems go dark.
What a Holistic Manufacturing Cybersecurity Approach Actually Looks Like
IBM’s own guidance on this, echoed across the industry, is that fragmented security, one plan for IT and a separate, less mature plan for OT, is the pattern that keeps producing bad outcomes. A more effective manufacturing cybersecurity approach treats IT, OT, and connected products as one environment to defend, with a few concrete priorities: visibility into every connected device, since you can’t protect what you don’t know exists; network segmentation, so a compromised IT account can’t reach the plant floor directly; and executive sponsorship that treats OT security as a business risk conversation, not a back-office IT ticket.
None of that is exotic. It’s disciplined, cross-functional work that most internal IT teams, especially ones sized for the office side of the business, aren’t staffed to take on alone. That’s where a partner with real OT visibility experience earns its place, bringing the specialized monitoring and segmentation work that turns “we hope the plant floor is fine” into an actual, defensible answer.